
Every business depends on technology to store information, communicate with customers, and manage daily operations. However, these valuable resources can become targets for cybercriminals if they are not properly protected. Computers, databases, software applications, and even employee accounts can create security risks when organizations fail to identify and manage them.
Understanding what assets are in cybersecurity is an important step toward protecting digital systems and sensitive business information. Cybersecurity assets include anything valuable to an organization that requires protection from security threats. This guide explains the meaning of cybersecurity assets, their different types, real-world examples, common security risks, and practical methods for effective asset management.
What Are Assets in Cybersecurity?
Assets in cybersecurity are valuable resources that an organization needs to protect from unauthorized access, damage, theft, disruption, or misuse. These resources may include physical devices, digital information, software applications, networks, and cloud services. Anything that supports important business operations or contains sensitive information can be considered a cybersecurity asset requiring appropriate security measures.
Cybersecurity assets are not limited to expensive equipment or advanced technology systems. A small business website, employee email account, customer database, or company laptop can also be a valuable asset. These resources often contain important information or provide access to other systems, making their protection necessary for maintaining secure business operations.
The main purpose of identifying cybersecurity assets is to understand what needs protection and why it matters. Organizations cannot effectively secure resources they do not know exist. By maintaining accurate information about their assets, businesses can recognize potential vulnerabilities, assign security responsibilities, and develop suitable protection strategies based on the importance of each resource.
Why Are Cybersecurity Assets Important?
Cybersecurity assets are important because they support the everyday activities that allow organizations to operate successfully. Businesses depend on computers, applications, communication systems, and stored information to complete essential tasks. If these resources become unavailable or compromised, employees may struggle to perform their responsibilities, potentially causing financial losses and operational disruption.
Protecting information assets also helps organizations maintain customer trust and business relationships. Personal records, payment information, confidential documents, and internal business data may contain details that should not be publicly accessible. Effective security controls reduce the likelihood of unauthorized disclosure and help organizations meet relevant privacy and information security responsibilities.
Asset identification also improves cybersecurity planning by showing where protection is most urgently needed. Not every resource carries the same level of risk or business importance. Understanding these differences helps security teams prioritize monitoring, access controls, software updates, and recovery arrangements instead of treating every system as equally critical.
Different Types of Assets in Cybersecurity
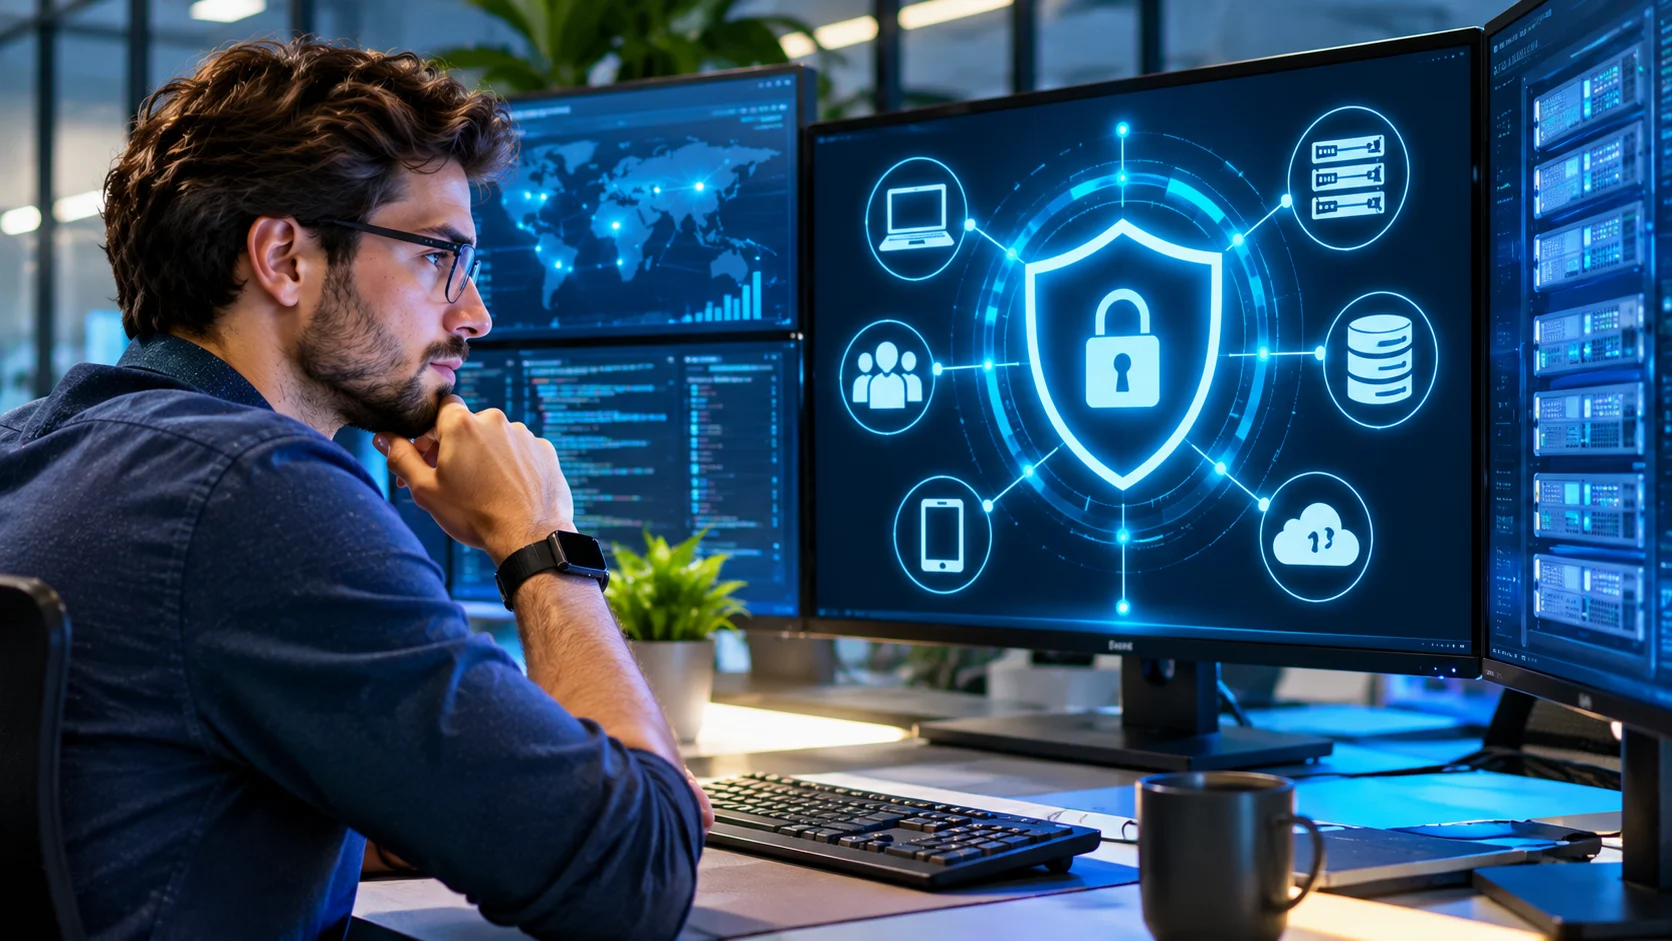
Cybersecurity assets can be divided into several categories based on their function and characteristics. Common categories include hardware, software, data, network infrastructure, cloud resources, and digital identities. Each type creates different security considerations, which means organizations need suitable protection methods rather than relying on one security solution for everything.
Physical assets include equipment such as computers, servers, smartphones, storage devices, and networking hardware. Digital assets include databases, software programs, documents, virtual machines, and online services. These categories often overlap because physical devices store digital information and provide access to applications that support daily operations.
Some organizations also recognize people, business processes, and external services as important assets within broader security and risk management activities. Employees possess valuable knowledge and use systems that require protection. Understanding how these resources interact helps businesses identify dependencies and develop a more complete picture of their overall cybersecurity environment.
Hardware Assets in Cybersecurity
Hardware assets are physical technology devices that organizations use to process, store, transmit, or access information. Common examples include desktop computers, laptops, servers, printers, smartphones, and external storage devices. These assets require protection because unauthorized access, physical theft, or equipment failure can expose information and interrupt important business activities.
Network equipment is another important category of hardware assets. Routers, switches, wireless access points, and firewalls help connect devices and manage communication across business networks. If these devices are configured incorrectly or contain security vulnerabilities, attackers may gain opportunities to intercept traffic, disrupt services, or access connected systems.
Protecting hardware assets involves combining physical security with appropriate technical safeguards. Businesses can use device encryption, secure passwords, software updates, access restrictions, and equipment inventories to reduce risks. Proper disposal is also important because old computers and storage devices may retain sensitive information unless their data is securely erased or destroyed.
Software Assets in Cybersecurity
Software assets include applications, operating systems, programs, and digital tools used to perform business activities. Examples include accounting software, customer management applications, email systems, web browsers, and business productivity platforms. These resources may contain sensitive information or provide access to important services, making them essential components of an organization’s cybersecurity strategy.
Software vulnerabilities can develop when applications contain programming weaknesses, outdated components, or insecure configurations. Cybercriminals may attempt to exploit these problems to access information or interfere with normal operations. Unsupported applications create additional concerns because vendors may no longer provide security patches that address newly discovered weaknesses.
Organizations can protect software assets through regular updates, appropriate access permissions, and reliable application management practices. Keeping an accurate software inventory helps identify outdated programs and unnecessary installations. Security teams should also review software suppliers, licensing arrangements, and configuration settings to reduce exposure to avoidable security risks.
Data Assets and Information Security
Data assets are collections of information that hold value for an individual or organization. Examples include customer records, employee information, financial statements, contracts, research documents, and intellectual property. These assets are especially important because unauthorized access or accidental disclosure can lead to privacy concerns, financial consequences, and damage to business relationships.
Data security focuses on protecting three important principles: confidentiality, integrity, and availability. Confidentiality means information is accessible only to authorized individuals, while integrity involves maintaining its accuracy and preventing unauthorized changes. Availability ensures that legitimate users can access necessary information when required to perform their responsibilities.
Protecting data assets involves using appropriate encryption, access controls, backup systems, and retention policies. Organizations should also identify where sensitive information is stored and who has permission to access it. Classifying data according to its importance helps businesses apply stronger safeguards to confidential records without unnecessarily restricting ordinary information.
Network and Cloud Assets in Cybersecurity
Network assets include the infrastructure and services that allow devices and applications to communicate. Examples include internal networks, wireless connections, firewalls, network management systems, and supporting communication services. These resources are important because they connect multiple business systems, meaning a security weakness in one area can sometimes affect other connected assets.
Cloud assets are resources hosted through cloud computing environments rather than maintained entirely on local equipment. They may include virtual servers, cloud storage, databases, software services, and application programming interfaces. Businesses often use these resources because they provide flexible access to computing services, but cloud environments still require careful security configuration and monitoring.
Cloud security responsibilities depend on the service model and the agreement between the customer and provider. Organizations generally remain responsible for protecting their information, managing user permissions, and configuring the services they control. Understanding shared responsibility helps prevent security gaps caused by incorrectly assuming that the cloud provider handles every aspect of protection.
Digital Identities and User Accounts as Security Assets
Digital identities represent users, devices, services, or applications that interact with an organization’s information systems. Employee accounts, administrator credentials, service accounts, and authentication systems are important security-related assets. These identities control access to valuable resources, making their protection essential for preventing unauthorized activity within business environments.
Compromised credentials can allow attackers to access systems while appearing to be legitimate users. Weak passwords, stolen login information, excessive permissions, and poorly managed accounts can increase this risk. Accounts with administrative access require particular attention because they may provide control over multiple applications, databases, or network settings.
Identity security includes strong authentication, appropriate account permissions, and regular access reviews. Multi-factor authentication provides an additional verification step that can reduce certain account compromise risks. Organizations should also remove unnecessary accounts and promptly update access permissions when employees change responsibilities or leave the business.
What Is Cybersecurity Asset Management?
Cybersecurity asset management is the process of identifying, recording, monitoring, and protecting the resources connected to an organization’s technology environment. It helps businesses maintain accurate knowledge of the devices, applications, services, and information they depend on. Effective asset management also provides useful information for vulnerability assessments, incident response, and routine security maintenance.
An asset inventory usually records details such as asset names, owners, locations, functions, and security classifications. For hardware, this may include device types, operating systems, and maintenance information. Software and cloud inventories may contain application versions, service providers, assigned permissions, and the business processes supported by each resource.
Asset management is an ongoing responsibility because business technology changes frequently. Employees receive new devices, applications are installed, cloud services are introduced, and outdated systems are retired. Regularly updating the inventory helps organizations identify unknown resources, reduce unnecessary exposure, and maintain reliable information about their overall security environment.
Asset Classification and Risk Assessment
Asset classification involves organizing resources according to their value, sensitivity, and importance to business operations. For example, publicly available website content may require different confidentiality controls from employee records or payment information. Classification helps security teams understand which assets need additional protection and which resources are essential for maintaining business continuity.
Risk assessment examines potential threats, vulnerabilities, and consequences associated with individual assets. A business might consider how likely a security incident is and what would happen if an important system became unavailable. This process helps identify priorities because an asset with sensitive information and weak security controls may require greater attention than a low-risk resource.
Organizations can use classification and risk assessment together to develop practical security plans. Critical assets may receive stronger authentication, enhanced monitoring, frequent backups, and additional recovery arrangements. However, classifications should be reviewed periodically because the importance of an asset can change as business operations, technology, and information requirements evolve.
Common Threats to Cybersecurity Assets
Malware is one of the common threats affecting hardware, software, and data assets. Malicious programs may attempt to steal information, interfere with system operations, or gain unauthorized control over devices. Ransomware is a particularly disruptive form of malware that can encrypt important files and interrupt access to essential business information.
Phishing and social engineering attacks create additional risks by targeting people rather than relying entirely on technical vulnerabilities. Attackers may use deceptive messages to persuade employees to reveal passwords, open harmful attachments, or provide confidential information. These incidents demonstrate why employee awareness and secure communication practices are important parts of asset protection.
Other threats include unauthorized access, software vulnerabilities, insider misuse, physical theft, and accidental data loss. Not every security incident involves a sophisticated cyberattack, since ordinary mistakes can also expose valuable resources. Understanding different threat categories helps organizations develop layered protection measures instead of relying on a single defensive technology.
Best Practices for Protecting Cybersecurity Assets
Protecting cybersecurity assets begins with maintaining an accurate inventory and identifying which resources support important business activities. Organizations should assign responsible owners, review asset classifications, and establish clear security policies. This foundation helps security teams understand what requires monitoring and makes it easier to recognize unfamiliar devices, applications, or services.
Strong access controls and regular software maintenance are also important security practices. Businesses should use appropriate authentication methods, restrict unnecessary permissions, and install relevant security updates promptly. Encryption, endpoint protection, network monitoring, and secure configuration settings provide additional safeguards that help reduce exposure to common cybersecurity threats.
Regular backups and incident response planning can help organizations recover when security problems occur. Backup copies should be protected from unauthorized changes and tested periodically to confirm that recovery procedures work. Employee training, routine security reviews, and appropriate supplier assessments also strengthen protection by addressing risks that technical tools alone cannot eliminate.
Conclusion
Assets in cybersecurity include the valuable resources that organizations use to store information, operate technology systems, and complete business activities. These resources include hardware, software, databases, networks, cloud services, and digital identities. Identifying them provides the foundation for understanding cybersecurity risks and developing appropriate protection measures across an organization’s technology environment.
Effective cybersecurity asset management involves maintaining accurate inventories, classifying resources, assessing risks, and assigning security responsibilities. Organizations should also protect their assets through strong authentication, regular updates, encryption, monitoring, and reliable backups. These practices reduce unnecessary exposure and support faster responses when technical problems or security incidents occur.
Understanding what assets are in cybersecurity is essential for businesses of every size. Even small organizations depend on valuable digital resources that require careful protection. By identifying critical assets and maintaining consistent security practices, businesses can strengthen their cybersecurity posture, protect sensitive information, and support more reliable daily operations.
Frequently Asked Questions (FAQs)
What is an asset in cybersecurity?
A cybersecurity asset is any valuable resource that requires protection from digital threats or unauthorized access. Examples include computers, software applications, databases, networks, cloud services, and employee accounts.
What are the main types of cybersecurity assets?
The main types include hardware, software, data, network infrastructure, cloud resources, and digital identities. Organizations may also consider people and important business processes within broader security asset management.
Why is asset management important in cybersecurity?
Asset management helps organizations identify valuable resources, understand security risks, and assign appropriate protection measures. It also supports vulnerability management, incident response, compliance activities, and business continuity planning.
What is the difference between an asset and a vulnerability?
An asset is something valuable that requires protection, such as a server or database. A vulnerability is a weakness that attackers may exploit to compromise the security of an asset.
How can businesses protect their cybersecurity assets?
Businesses can protect assets through accurate inventories, strong authentication, regular software updates, encryption, access controls, monitoring, and reliable backups. Employee awareness training and periodic security assessments provide additional protection.